
Why doesn't Bitcoin need banks? UTXO, nodes, PoW
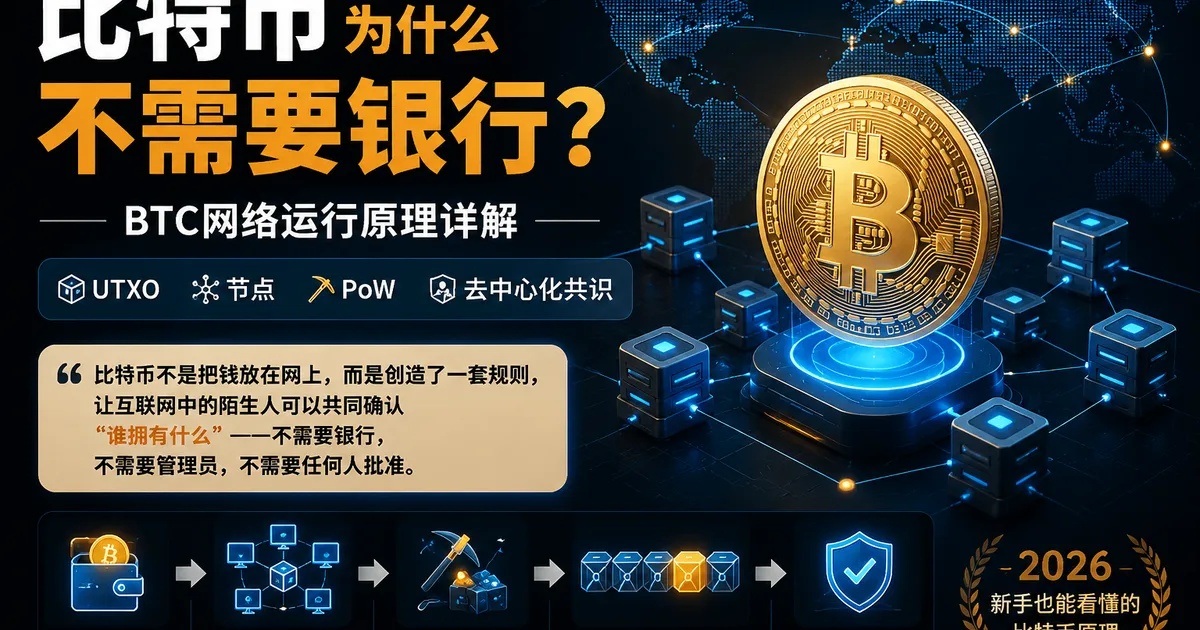
Table of contents

Binance new user rewards
20% trading fee rebate
Official Binance registration. Complete identity verification (KYC) to trade and withdraw.
Bitcoin isn't putting money on the internet — it's creating a set of rules that let strangers on the internet jointly confirm "who owns what" — no bank, no administrator, no one's approval needed.
If all the banks in the world shut down tonight, could the Bitcoin network still transfer money?
The answer is: yes.
But the deeper question is: what problem did it solve that traditional computer science couldn't?
The bank's job, on the surface, is "keeping your money safe." But in essence, the bank maintains a centralized state about "who owns how much." That state lives in the bank's database, and the bank has the power to change it.
Bitcoin's real innovation isn't creating a "digital currency" — it's the first time tens of thousands of mutually untrusting nodes around the world jointly maintain a history that no one can freely rewrite, without a central database administrator.
Computer science has a concept called a state machine — a system starts from an initial state, and each transaction changes the state once. The bank is the sole administrator of this state machine. Bitcoin removes that administrator.
This leads to the core questions this article answers:
- Without an administrator, who decides how the "state" changes?
- Without anyone keeping a balance table, how do you prove "how much you have"?
- If someone tries to rewrite history, how does the system resist?
- Why hasn't this system collapsed after 15 years?
This article takes the design apart in a beginner-friendly way. No formulas, no code — just explaining why it's designed this way.
One important clarification up front: Bitcoin isn't without governance — it just has no single administrator with final coercive control. Full nodes maintain the rules, developers maintain the code, miners provide the security budget — three parties check and balance each other, and no one can unilaterally call the shots.
This article is technical education only and does not constitute any investment advice.
It's recommended to first read What is Bitcoin (BTC)? Principles, value and risks (2026), then come back — this article will read more smoothly.
What does a bank maintain? How Bitcoin replaces it
On the surface, a bank "keeps your money safe." But what a bank really does is maintain a centralized state database:
Bank database (centralized state):
  Alice: 3 BTC
  Bob:   0.5 BTC
  …
This database has three characteristics:
- The bank is the only administrator — only it can change this state;
- You can only trust it — you can't see inside the database, you can only believe the balance it tells you is correct;
- The bank can be influenced by outside forces — regulatory requirements, court rulings, internal decisions, all can change your account state.
What Bitcoin does is overturn all three of these:
| Traditional finance (centralized state machine) | Bitcoin (decentralized state machine) |
|---|---|
| A single administrator maintains the state | Tens of thousands of full nodes jointly maintain the state |
| Trust an institution not to act badly | Trust code rules and economic incentives |
| Outside forces can intervene | Changing state requires PoW proof + network-wide consensus |
| A balance is a number in a database | A "balance" is a pile of unspent digital ownership proofs (UTXO) |
| Security comes from law, police, courts | Security comes from "cost of attack > benefit of attack" |
Bitcoin isn't "no bank" — it's reimplementing the bank's role as "state administrator" using a set of rules anyone can verify.
A bank actually plays three roles, and Bitcoin replaces each one:
Role one: state maintainer. The bank records "who has how much money." Bitcoin's replacement: it doesn't record balances, only "transaction outputs that haven't been spent yet" (UTXO), which anyone can verify independently.
Role two: transaction auditor. The bank checks signatures and balances. Bitcoin's replacement: cryptographic digital signatures + full nodes independently verifying every transaction.
Role three: rule enforcer. The central bank decides the issuance amount. Bitcoin's replacement: rules written in code (21 million coins + halving), changed only through network-wide consensus.
This isn't eliminating trust — it's redistributing trust — from trusting "an institution won't act badly" to trusting "public rules and self-interested incentives make acting badly unprofitable."
Bitcoin has no "balance", only digital ownership proofs (UTXO)
This is the most fundamental technical difference between Bitcoin and banks.
Bank: a balance table
Account Alice: 1.0 BTC
Account Bob:   0.5 BTC
Alice sends 0.3 BTC to Bob → Alice minus 0.3, Bob plus 0.3. Two UPDATE rows, done.
Bitcoin: a pile of unspent ownership proofs
Bitcoin's ledger has no "balance" field.
It records UTXOs — Unspent Transaction Outputs. The essence of each UTXO is:
"There exists a digital object worth X BTC on the network, and only someone meeting a specific condition (usually a signature from a specific private key) can unlock it."
Your "balance" is the sum of the face values of all UTXOs whose unlock condition is your address.
A concrete example
Alice previously received a transaction, and the network now has a UTXO:
UTXO #837291:
  Face value: 1 BTC
  Unlock condition: requires Alice's private key signature
Now Alice wants to send Bob 0.3 BTC. What actually happens:
New transaction:
  Input: UTXO #837291 (the whole 1 BTC is consumed)
  Output #1 → Bob: 0.3 BTC (unlock condition: Bob's private key signature)
  Output #2 → Alice change: 0.7 BTC (unlock condition: Alice's private key signature)
Two key points:
- A UTXO must be fully consumed. It's like paying for a $30 item with a $100 bill — you must hand over the whole $100 bill and receive $70 in change. You can't "spend only $30 of the $100."
- Each UTXO is an independent digital ownership proof. Alice doesn't "have a 1 BTC balance" — she "holds a digital ownership proof worth 1 BTC, and only she can unlock it." After spending, that proof is destroyed and two new proofs are created (0.3 → Bob, 0.7 → Alice).
Why Satoshi chose UTXO instead of the account model
| Account model | UTXO model | |
|---|---|---|
| Essence | A number recording a balance | A pile of independent digital ownership proofs |
| Concurrency | Needs table locks to prevent double-spending | Each UTXO can only be spent once, naturally preventing double-spending |
| Privacy | Balance is transparent to the administrator | Different UTXOs can be linked to different addresses |
| Verification | Trust the administrator's calculation | Anyone can independently verify each UTXO's validity |
| Philosophy | "You have X in your account" | "You hold N digital objects waiting to be unlocked" |
The UTXO model means Bitcoin needs no "account administrator." No one needs to tell you "how much you have" — your wallet scans the blockchain, finds all UTXOs whose unlock condition is your address, adds them up, and shows it as your "balance."
On wallets and private keys, see What is a crypto wallet? Wallet addresses, seed phrases and asset safety (2026).
The distributed ledger: why many copies are safer than one
Bank model: one server, one ledger.
User → bank server → single database
The attack target is clear: breach that database.
Bitcoin model:
Node1  Node2  Node3  Node4  ……  NodeN
  │      │      │      │         │
  └──────┴──────┴──────┴─────────┘
     All full nodes following the same rules
     agree on the valid block history
Key differences:
- There's no "master ledger" — every copy is equal.
- Someone secretly edits their own copy? Other nodes don't recognize it, so the edit is useless.
- Rewriting history requires breaching most nodes at once + passing consensus verification — the cost is unrealistically high.
An analogy: a class of 50 students each holds an identical transcript. Someone changes their own 40 points → 90 points? The other 49 transcripts show 40, so no one accepts it.
Decentralization isn't "giving everyone a backup" — it's making it impossible for any single point to define the truth.
For more blockchain details, see What is blockchain? Principles, uses and risks (2026).
Block + chain: databases solve efficiency, Bitcoin solves trust
Some ask: if you need to store data, why not just use MySQL?
Because a database and Bitcoin solve two completely different problems.
| Database | Bitcoin blockchain | |
|---|---|---|
| Optimization target | Query and write speed | Immutable history |
| Who can change it | An authorized administrator | Anyone who wants to change it must redo the PoW |
| Trust model | Trust the administrator not to err or act badly | Trust no one, only verify rules |
| In one sentence | Solves the efficiency problem | Solves the trust problem |
An ordinary database:
Administrator → UPDATE one row → data changed (milliseconds)
Bitcoin:
Build transaction → cryptographic signature → full-node verification →
miner packs it → PoW proof → added to irreversible history (10+ minutes)
History is trustworthy not because it's "stored in a database," but because: changing the past requires re-proving all the computational work of the future. This is a trust mechanism, not a storage solution.
Block: an untearable page of the ledger
Each block contains: a batch of transactions + block height + the previous block's hash + timestamp + nonce.
Chain: the chemical bonds between pages
Each block stores the previous block's hash. Like page 10 having page 9's summary printed on it. Change page 5 → page 6's summary no longer matches → page 7 doesn't match → the whole book is void.
Why records are so hard to tamper with
Suppose someone wants to tamper with a transaction in block 800000:
- Change block 800000 → its hash changes.
- Block 800001's stored "previous hash" no longer matches → recompute 800001.
- 800001's hash also changes → recompute 800002.
- And so on, recomputing every block after it.
- While recomputing, the whole network's miners are still producing blocks on the original chain → you must outrun the network's total hash rate.
- Even if you win → the new chain must still be accepted by tens of thousands of full nodes. A different chain is simply rejected.
The precise meaning: tampering requires rebuilding every block after the tampered one + exceeding the network's total honest hash rate — the economic and time cost is unrealistically high, not mathematically impossible.
This is why confirmation count matters: the more confirmations, the deeper a transaction is "buried," and tampering cost grows exponentially.
Consensus: what PoW buys isn't bookkeeping rights, but attack cost
With no central authority, who decides which version is correct?
The intuition: voting. Every node gets one vote.
The fatal flaw: Sybil attacks. One computer can fabricate a million fake nodes. One computer = a million votes. "Voting by headcount" is meaningless in a decentralized network.
Satoshi's choice: replace voting with unforgeable real cost
Bitcoin's answer: prove your right to participate in consensus with unforgeable real-world resource commitment.
That's PoW (Proof of Work):
- Miners buy ASICs (hardware cost) + burn electricity (operating cost), brute-forcing nonces.
- Find a valid hash → earn the right to pack a block + the block reward.
- Forge a block → full nodes reject it → the hash power is wasted.
- Mining honestly is more profitable than cheating.
The real economics of PoW: what it buys is attack cost, not bookkeeping rights
This is the most important perspective shift for understanding PoW.
A traditional bank's security model:
Law → police → courts → regulation
(multiple layers of social mechanisms protecting the centralized state)
Bitcoin's security model:
Cost of attack > benefit of attack
(pure economic calculation, not relying on any external enforcement)
An attacker isn't "unable" to attack — it's that the cost of attacking Bitcoin (ASICs + electricity + time) exceeds the benefit they could get from a successful attack. And once an attack is detected, Bitcoin's price crashes, and the BTC and mining machines the attacker holds depreciate together — the attack cost is real, and the benefit could go to zero.
So the energy PoW consumes isn't wasted — it's buying the security property of "making attacks unprofitable." According to the Cambridge Bitcoin Electricity Consumption Index (CBECI), Bitcoin's annual network energy consumption is roughly equal to a medium-sized country — that electricity is essentially maintaining the "attacks aren't worth it" threshold. But it must also be admitted: this security model means Bitcoin must continuously consume energy to maintain attack cost, which is PoW's core controversy. Security mechanism = cost mechanism; the two are fused into one in PoW.
If you're interested in the full picture of crypto security, see Crypto beginner scam prevention: 5 scams I've seen and 1 life-saving principle — the Bitcoin protocol itself has security boundaries, but the scams and risks around it are another matter.
"Longest chain" is really "greatest accumulated work"
The everyday phrase "longest chain" isn't precise enough. Full nodes choose the chain with the highest accumulated PoW difficulty, not simply the one with the most blocks. In 99% of cases the two coincide, but the precise statement should be "the greatest accumulated work principle."
Why 6 confirmations are considered safe
Explain it with a double-spend attack scenario:
Step one: the attacker uses a UTXO to pay a merchant 1 BTC. The transaction is broadcast to the network.
Step two: simultaneously, the attacker secretly creates another chain — the same UTXO sent back to their own other address. They quietly mine on this secret chain.
Step three: the merchant sees 1 confirmation and ships the goods. But the attacker's secret chain has already mined 2–3 blocks.
Step four: the attacker broadcasts the secret chain. If its accumulated work > the public chain, full nodes switch — the transaction paying the merchant "disappears."
Confirmation count is a multiplier of attack cost
The attacker has to generate an alternative chain with more work, starting from the block containing the payment transaction. Each additional confirmation means the attacker is one block further behind, so the work they need to catch up is greater.
But one important clarification: even if an attacker controls 51% of the hash rate, they cannot:
- Steal other people's BTC (no private key, can't sign);
- Create Bitcoin out of thin air (violates issuance rules, full nodes reject it outright);
- Modify any arbitrary transaction in historical blocks (would require recomputing from the target block to the latest — enormous work).
What they can do: reorganize recent transactions (double-spend their own coins) and block specific transactions from being confirmed.
Exchanges requiring 2–6 confirmations is precisely to make this kind of attack economically unviable. Confirmation count isn't a guarantee of safety — it's a multiplier of attack cost.
Bitcoin's four-layer power structure
Many people get one thing wrong: miners ≠ Bitcoin's controllers.
Bitcoin's real power structure is a four-layer balance:
Layer one: ownership — "is this BTC yours?"
Tools: private key, public key, digital signature.
You sign with your private key → the whole network verifies with your public key → no one can derive the private key from the signature. No bank needs to verify your identity — cryptography answers the ownership question directly.
Layer two: propagation — "how does a transaction become known to the whole network?"
Tools: P2P network, gossip protocol, mempool.
Nodes forward transactions and blocks like a game of "telephone." There's no central server; messages spread automatically between nodes. No need to rely on an interbank messaging network to settle.
Layer three: ordering — "who records first, and on what basis?"
Tools: PoW, full-node verification, the greatest accumulated work principle.
One key fact: miners are not the judges — full nodes are. Miners only pick and order from the pool of already-verified legitimate transactions — a transaction's legitimacy is judged independently by full nodes. If a miner packs a non-compliant transaction, full nodes reject the entire block, and the hash power the miner invested is wasted.
One easily overlooked but astonishing fact: if you install Bitcoin Core on your own computer, it will do the following — download the entire ~600 GB blockchain history → verify block by block from the genesis block → verify the signature of every transaction → build the complete UTXO set → and in the end, your computer gains the complete ability to independently judge "which chain is real."
An ordinary person, on a home computer, can independently verify 15 years of global financial history — trusting no one. This is closer to Bitcoin's essence than the word "decentralization" itself. For a more complete beginner learning path, see New to crypto? Learn in this order to avoid detours.
Layer four: maintenance — "why would anyone run this system?"
| Participant | Gives | Gets |
|---|---|---|
| Miners | ASICs + electricity + operations | Block rewards + fees |
| Full nodes | Storage, bandwidth, operations | Independent verification rights, no reliance on third parties |
| Users | Fees | Permissionless global transfers |
| Developers | Code maintenance time | Community influence, funding |
Bitcoin doesn't run on altruism. It makes self-interested behavior produce altruistic results — miners mine honestly to earn, nodes sync full data for independent verification, users pay fees for transfer freedom.
The four layers connected
Ownership (cryptography)
   ↓
Propagation (P2P network)
   ↓
Ordering (PoW + full-node rule enforcement)
   ↓
Maintenance (economic incentives)
   ↓
A globally consistent, immutable state
But theory is theory — does this power structure actually hold up in reality? The next chapter answers with real history.
What happens in 10 minutes when you send 0.1 BTC
| Time | Event | Layer |
|---|---|---|
| 0 s | Alice enters Bob's address and 0.1 BTC, taps send | — |
| < 1 s | The wallet picks Alice's available UTXOs as inputs and signs with her private key. It constructs outputs: 0.1 → Bob, remainder → Alice's change address | Ownership |
| A few seconds | The transaction broadcasts to nearby nodes. Nodes first verify independently: signature valid? UTXO exists and unspent? input ≥ output? Only if it passes does it enter the mempool | Propagation |
| Tens of seconds | The gossip protocol spreads it network-wide; every node that receives it does the same verification | Propagation |
| 1–10 min | Miners pick already-verified legitimate transactions from the mempool by fee, pack them into a candidate block, and brute-force nonces | Ordering |
| ~10 min | A miner finds a valid nonce and broadcasts the new block | Ordering |
| < 1 s | Full nodes receive the new block and independently verify every transaction again | Ordering |
| Verification passes | The new block is added to the chain; the transaction gets 1 confirmation | Ordering |
| ~60 min | The next 5 blocks are mined, totaling 6 confirmations | Ordering+Maintenance |
Key details:
- Before miners pack it, nodes have already verified it. Miners don't "approve" transaction legitimacy — they only pick and order from the verified pool.
- 0 confirmations = the transaction is still in the queue, not settled.
- The higher the fee → the more likely a miner packs it first.
The four trade-offs Bitcoin made
| Gained | Sacrificed | Why this choice |
|---|---|---|
| Decentralization (no single point of control) | Speed (~7 TPS vs VISA's 24000) | Large settlements don't trade for "fast"; daily payments go through the Lightning Network |
| Security (immutable history) | Energy (≈ a medium-sized country) | Security mechanism = cost mechanism; PoW's energy is the security budget |
| Censorship resistance (no one can freeze) | Governance efficiency (upgrades need long consensus) | The SegWit case in the next chapter is the best example |
| A globally unified ledger | Limited on-chain throughput (~1–3 MB/block) | The main chain is a secure settlement layer; layer 2 is the high-frequency payment layer |
Bitcoin isn't incapable of being faster and cheaper — it deliberately chose slow but safe, expensive but irreversible, hard to change but stable.
The 2017 SegWit war: a real test of power
Earlier I said "full nodes matter more than miners" and "developers can't unilaterally change rules." This isn't theoretical deduction — a real power struggle happened in 2017.
Background
Bitcoin faced a scaling problem: blocks were nearly full, transactions slowed, fees rose.
Two camps:
- Big-block camp (miner-led): directly expand blocks from 1 MB to 8 MB, simple and crude;
- SegWit camp (Core developer-led): optimize the transaction data structure through a soft fork, separating signature data out, indirectly scaling to about 2–3 MB — while paving the way for the Lightning Network.
The power struggle
Large mining pools and large miners publicly backed the big-block plan. By "whoever has the hash power calls the shots" logic, miners should have won.
But what actually happened:
- Full-node operators refused to upgrade to the big-block version. Because bigger blocks → higher cost to run a node → lower decentralization, which conflicts with their core interest.
- Users expressed their position by running SegWit-supporting nodes. Node count is voting power, not hash power.
- Developers insisted on not merging the big-block plan into Bitcoin Core. Miners could fork the code and go their own way, but they'd lose the Core developers' technical credibility, and the new chain's value would be in doubt.
- In the end, the miners compromised. SegWit activated in August 2017 (see BIP 141). The big-block camp later forked into Bitcoin Cash (BCH) — but to this day BCH's market cap, hash rate and node count are not in the same league as BTC's.
What this case proves
Bitcoin's governance isn't "hash power calls the shots," nor "developers call the shots" — it's a multi-layer balance among rule enforcers.
- Miners hold hash power, but full nodes hold the ultimate power of "rejecting blocks that don't follow the rules."
- Developers can write code, but miners and full nodes can choose not to run the new version.
- Users can freely choose which version of the node to run — that itself is a form of voting.
This exactly confirms the article's core point: Bitcoin has no single administrator. Power is dispersed among miners, full nodes, developers and users; any party that wants to unilaterally change the rules will face resistance from the others.
Why the Bitcoin protocol has long-term stability
The SegWit case above shows Bitcoin's balance of power. But there's an even more fundamental angle: why does this system grow more stable, not more fragile, over time?
The answer isn't in investment narratives, but in five stability anchors of the protocol itself:
| Stability anchor | Why it matters |
|---|---|
| Full-node count | About 15,000–20,000 reachable full nodes worldwide. More nodes → more rule enforcers → harder to rewrite history |
| History depth | 15 years of uninterrupted block history. Each additional day alive accumulates one more day of trust. A new chain can't fake time |
| Incentive compatibility | Miners, nodes, developers, users — four parties with different interests but aligned behavior. Honest behavior is the most favorable choice for each party |
| Software compatibility | Bitcoin Core stays backward compatible. A transaction format from 15 years ago is still valid today. This stability is itself a trust asset |
| Social coordination cost | Changing core rules requires four-party consensus (like the SegWit case). Coordination cost is extremely high → rules are extremely stable. Many want to change the rules; very few can |
The first two are "physical anchors" — objectively measurable. The last three are "social anchors" — repeatedly verified in real historical events.
These five anchors together make up Bitcoin's long-term stability. It's not "won't fail," but the probability of failure keeps declining over time — this is the technical explanation of the Lindy effect.
Why copying Bitcoin's code doesn't copy Bitcoin
Bitcoin is open source. Anyone can fork the code, tweak a few parameters, and launch a "new Bitcoin" in 5 minutes.
Of thousands of copies, none comes close to Bitcoin.
Because five things can't be copied:
1. Hash-power security
The network's ~600 EH/s of SHA-256 hash power accumulation. A new chain has no miners willing to switch hash power over — the token isn't worth anything, and mining it would produce coins they can't sell.
2. History depth
15 years of uninterrupted block history. A new chain's "history" starts from zero; time accumulation can't be compressed.
3. Social consensus
Exchanges, wallets, custody, ETFs, media, hundreds of millions of users — the cognitive and infrastructure investment forms an enormous network effect. Code can be forked; consensus can't.
4. Incentive compatibility
Bitcoin's four-party interest structure (miners, nodes, developers, users) is a balance evolved over 15 years. Copies either have flawed incentive design or are highly centralized from the start.
5. The Lindy effect
The longer it survives → the more likely it keeps surviving. Bitcoin has weathered multiple bull-bear cycles, bans from many countries, and countless "Bitcoin is dead" declarations — this antifragility can't be obtained overnight by a new project.
The real moat: the combination of code + hash power + time + consensus + incentive compatibility. None of it can be Ctrl+C / Ctrl+V'd.
What "decentralization" actually removes — and three real lessons
Three things removed
Single-point bookkeeping: a bank can freeze an account; no one on the Bitcoin network can freeze an address.
Single-point approval: sending BTC abroad needs no one's approval. A private key is enough.
Single-point failure risk: if a server goes down, you can't transfer. Bitcoin runs as long as there are still nodes and miners online anywhere in the world.
But decentralization isn't absolute
Hash power is concentrated in a few large mining pools. Code maintenance is concentrated in a few core developers. Most BTC sits on centralized exchanges.
Decentralization is a matter of degree, not a switch.
Three real events, understanding the boundaries of decentralization
Event one: the 2014 Mt. Gox collapse (exchange vs protocol)
Mt. Gox was once the world's largest Bitcoin exchange, and collapsed in 2014 claiming 850,000 BTC was "stolen."
Many said at the time "Bitcoin was hacked" — that's wrong.
The Bitcoin protocol was never breached. It was Mt. Gox's private-key management failure — an internal security problem of a centralized service. The protocol's decentralization ≠ the decentralization of every service that uses Bitcoin. Today, if you keep BTC on a centralized exchange, you face the same platform risk — which is a different matter from whether the Bitcoin protocol is secure. On identifying and guarding against such risks, see Crypto beginner scam prevention: 5 scams I've seen and 1 life-saving principle.
Event two: the 2010 overflow bug (protocols err too)
Bitcoin had a serious bug early on (CVE-2010-5139): one transaction created about 184 billion BTC (far beyond the 21 million cap).
Satoshi and the developers released a fix within hours, and the community quickly upgraded their nodes. That "wrong chain" was abandoned.
This shows: Bitcoin wasn't perfect from day one — it grew step by step through public operation, consensus upgrades and community coordination. Bugs appear; the key is whether they're fixed in time after discovery, and whether the fix mechanism is healthy.
Event three: what a 51% attack can and can't do (security boundaries)
Earlier I said a 51% attacker can double-spend their own coins and block transactions. But they can't steal others' coins, can't create coins out of thin air, can't change issuance rules. Because full nodes reject any block that violates the rules — no amount of hash power helps.
These three events respectively show: the security of the Bitcoin protocol ≠ the security of the services around it; Bitcoin isn't perfect but has self-repair mechanisms; Bitcoin's security boundaries are publicly verifiable, not dependent on anyone's promise.
The overall architecture of the Bitcoin network
A text version of the architecture diagram — one image to see the whole system's operating logic:
              │  You initiate a transaction
              │  (wallet signs with your private key)
              ↓
    ┌─────────────────────┐
    │  Layer 1: ownership  │
    │  cryptography        │
    │  (signature + pubkey) │
    │  → proves you can spend this UTXO │
    └─────────┬───────────┘
              ↓
    ┌─────────────────────┐
    │  Layer 2: P2P spread │
    │  gossip + mempool    │
    │  → tx spreads to nodes │
    └─────────┬───────────┘
              ↓
    ┌─────────────────────┐
    │  Full nodes verify   │
    │  sig, UTXO, no double│
    │  spend → rule enforcers│
    │  (not miners)        │
    └─────────┬───────────┘
              ↓
    ┌─────────────────────┐
    │  Layer 3: PoW ordering│
    │  miners compete → pack│
    │  → most-work chain wins│
    └─────────┬───────────┘
              ↓
    ┌─────────────────────┐
    │  Irreversible history│
    │  each block locks prev│
    │  → tamper = rebuild all│
    └─────────┬───────────┘
              ↓
    ┌─────────────────────┐
    │  Layer 4: incentives │
    │  reward+fees → miners │
    │  verify rights → nodes│
    │  → self-sustaining   │
    └─────────┬───────────┘
              ↓
    ┌─────────────────────┐
    │  Global immutable state│
    │  15 yrs, tens of thousands│
    │  of nodes in consensus │
    └─────────────────────┘
The point of this diagram: full-node verification happens before miners pack. Miners don't approve transactions — they only order already-verified legitimate transactions. Many people get this order backwards.
The concepts beginners most often confuse
Misconception one: "Bitcoin runs on servers"
Wrong. It runs on tens of thousands of nodes worldwide, with no central server.
Misconception two: "Miners control Bitcoin"
Wrong. Miners handle ordering; full nodes enforce the rules. Miners aren't the judges — full nodes are. The 2017 SegWit war already proved this — large mining pools collectively backed the big-block plan, and in the end it was the users and full nodes who decided.
Misconception three: "Bitcoin is too slow, so it doesn't work"
~7 TPS isn't fast, but that's a design choice — speed traded for security. Daily payments go through the Lightning Network; large settlements go through the main chain. Different scenarios use different layers.
Misconception four: "Decentralization = zero trust"
Wrong. It's shifting trust from "institutions" to "code + incentives." You still need to trust SHA-256's security, miners' rationality, and your own ability to keep your private key safe. Trust changes form; it doesn't disappear.
On private keys, see What is a seed phrase? Why no one can recover your assets if you lose it (2026).
Misconception five: "Bitcoin has been hacked"
The 2014 Mt. Gox case was an exchange's private-key management failure, not a breach of the Bitcoin protocol. The protocol's decentralization ≠ the decentralization of services. Your BTC on a centralized exchange is as secure as that exchange — not as secure as the Bitcoin protocol.
FAQ
Bitcoin has no "balance" — what is the number my wallet shows?
Your wallet scans all UTXOs on the blockchain whose unlock condition is your address, and adds up their face values. The "balance" you see is the sum of a pile of independent UTXOs — not a database number. The wallet does this addition for you, but at the bottom there's no "balance" concept.
Why PoW instead of voting?
Node count can be forged at zero cost — one computer running a million fake nodes (Sybil attack). PoW replaces identity voting with unforgeable real cost (hardware + electricity). Every unit of hash power has real money behind it and can't be mass-produced.
Miners vs full nodes — which matters more?
Full nodes are the referees; miners are the athletes. Full nodes verify whether every transaction and block is compliant — and reject non-compliant ones outright. Miners only pick and order from the pool of already-verified legitimate transactions. Without full nodes, no one checks whether miners cheat; without miners, no one provides the security budget. Both are indispensable, but the final power of rule enforcement lies with full nodes. The 2017 SegWit war already proved this with real history.
Why would anyone run a full node for free?
People who run full nodes aren't doing charity. What they get is independent verification rights — not needing to trust any third party to tell them "this chain is real." Exchanges, payment providers and large holders run full nodes to independently verify their own asset security. This is a "self-protection incentive" — self-interested behavior produces an altruistic result (a more decentralized network).
Will quantum computers destroy Bitcoin?
Practical quantum computers don't exist yet. Even if they appear in the future, the community has a path to upgrade to quantum-resistant signatures (like Lamport signatures), requiring a network-wide soft fork or hard fork. Technically feasible, but coordination is complex. Not something to panic about today.
Is Bitcoin mining a waste of electricity?
PoW's energy use is a deliberate design of the security model — energy consumption = the threshold of attack cost. But this also means Bitcoin must continuously consume energy to maintain security, which is PoW's core controversy. Supporters see it as a necessary security budget; critics think it's too inefficient. The mining industry is also pushing renewable and stranded energy. There's no simple answer, but the fact that security mechanism = cost mechanism is the key to understanding PoW.
Summary
Bitcoin isn't putting money into the internet — it's the first time in human history that mutually untrusting nodes around the world have jointly maintained a history that can't be freely rewritten, without an administrator.
It's a decentralized state machine. The bank is traditional finance's "state administrator," and Bitcoin replaced it with a four-layer power structure:
Ownership (cryptography proves "you have the right to spend")
   ↓
Propagation (P2P broadcasts transactions to the world)
   ↓
Ordering (PoW + full-node rule enforcement: miners order, nodes judge)
   ↓
Maintenance (economic incentives keep all four parties voluntarily participating)
   ↓
A globally consistent, immutable history
These four layers aren't a hierarchy — they're mutually balancing — as the 2017 SegWit war proved, even if large mining pools collectively push a change, if full nodes and users don't buy in, the change can't be force-activated.
Bitcoin paid four costs for this design: speed, energy, governance efficiency, and on-chain throughput. These aren't flaws — they're conscious choices.
Bitcoin's real moat isn't the code (code can be copied), but the combination of hash power + time + consensus + incentive compatibility + the Lindy effect. These accumulated over 15 years of evolution, not a 5-minute fork.
One sentence to remember this article:
Bitcoin isn't putting money on the internet — it's creating a set of rules that let mutually untrusting people reach agreement on "who owns what" — no bank, no administrator, no one's approval needed. And these rules have been running automatically on tens of thousands of nodes worldwide for 15 years.
Related reading
- What is Bitcoin (BTC)? Principles, value and risks (2026) — BTC basics
- How does the blockchain record transactions? Blocks, hashes, proof of work (2026) — next in the series
- What is blockchain? Principles, uses and risks (2026) — full blockchain overview
- New to crypto? Learn in this order to avoid detours — beginner learning path
- What is a seed phrase? Why no one can recover your assets if you lose it (2026) — private key security
- What is a crypto wallet? Wallet addresses, seed phrases and asset safety (2026) — wallet basics
Disclaimer
This article is for Bitcoin technical education only and does not constitute any investment, financial or trading advice.
Crypto asset prices are highly volatile, and related services may carry platform risk, market risk, network security risk and operational risk. Users should judge carefully according to their own risk tolerance and follow the laws and regulations of their location.
Any behavior involving private-key management, transfer operations or asset custody should fully understand the risks first, then test with a small amount.
- Bitcoin Whitepaper — Satoshi NakamotoThe whitepaper original, basis for the UTXO and PoW design
- Bitcoin.orgExplanation of Bitcoin's basic concepts and how it works
- Bitnodes.ioAbout 15,000–20,000 reachable full nodes worldwide
- Cambridge Bitcoin Electricity Consumption Index (CBECI)Estimate of the network's annual energy consumption
- Blockstream SatelliteBroadcasting on-chain data without an internet connection
See ourEditorial Policy and the correction process in ourCorrections Policy.
The CoinTrailHub editorial team focuses on crypto education for beginners, exchange security and P2P trading risk. This article is compiled from official sources and public data, reviewed by humans, and strives for accuracy but is not investment advice.
Last updated:2026-08-05 · Content reviewed by humans · Learn more
© 2026 CoinTrailHub · Original content. Reproduction or rewriting without permission is prohibited.